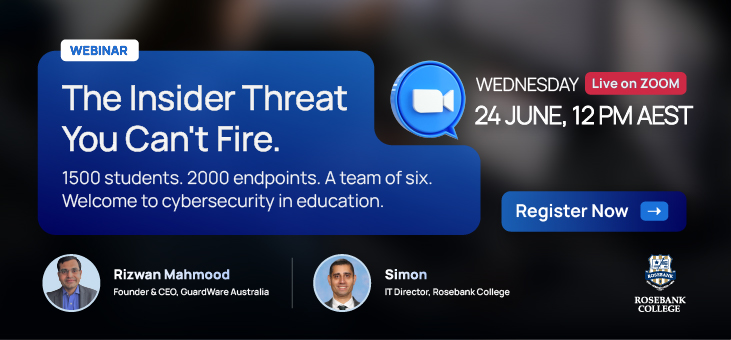
In a recent GuardWare webinar, our CEO Rizwan Mahmood sat down with Andrew Hottes, CEO of ISO4 and the leader behind the first school in the world to achieve ISO 42001 certification for AI management. Their conversation covered what good governance looks like in education, how to manage AI responsibly, and where any school can start. Here are the key takeaways.
Why ISO4 exists
Andrew spent 13 years in global CIO roles across the UK, US and Hong Kong before moving into education, and saw how differently large organisations and schools are resourced for governance, risk and compliance. That gap shaped his mission:
“Good governance should not just be affordable. It shouldn’t be the domain of just the big enterprises. It should be available to everyone.”
The gap is a system, not a shortage of care
Schools invest heavily in firewalls, endpoint protection, backups, and monitoring. What is often missing is the governance that connects these tools together. Who owns a particular information risk? Where is the evidence that a control is working? When were backups last tested?
“The gap is not lack of care. It’s not lack of capability. It might be a lack of time, but it’s an absence of a repeatable system.”
When a good intention such as “we will test our backups monthly” becomes an accountable, measurable activity, governance starts to deliver real protection. As Andrew put it:
“A firewall without governance is just a firewall.”
Ownership, classification, and regular reviews
Good data governance starts with clear owners and clear classification, so everyone knows what they are dealing with. Role based access keeps permissions appropriate, and a periodic review keeps them that way. Even a review once every six months, to remove access when staff change departments or roles, can significantly reduce exposure. Permissions quietly accumulate over time, and a simple, regular review is one of the most effective ways to stay ahead of that.
Visibility comes first, especially with AI
Many schools have adopted tools like Copilot while teachers also explore other AI tools for research and curriculum planning. Rather than trying to block everything, which limits innovation and learning, the most effective approach starts with visibility. As Andrew explained:
“If you don’t know what sensitive data you hold and where it is, and you don’t have visibility of how it moves within your organisation, you’re trying to control something you cannot see.”
Bringing staff along matters too. When teachers understand why a control exists and what it protects, security becomes a shared goal.
“When teachers understand consequence rather than restriction, the conversation becomes very different.”
Looking beyond your own walls
Recent third party breaches, including the Canvas incident, are a reminder that a school can do everything right internally and still be exposed through a supplier.
“You can do so much internally and still be exposed through a supplier.”
A strong starting point is a complete application and supplier register covering what data each vendor holds, how it is protected, who can access it, and whether AI features have been reviewed. As Rizwan noted during the session, you can’t protect what you don’t know you have.
Speaking the board’s language
Cyber risk is a whole of organisation risk, not only an IT concern. Boards do not need a list of vulnerabilities. They need to know which information and services are most critical, who owns them, what controls are in place, and where gaps remain.
“It’s not an IT responsibility or risk. It’s a whole of organisation risk.”
Mapping to a recognised standard such as ISO 27001 gives boards a clear, credible way to understand and demonstrate their position. It also helps in another way: if a threat actor can’t get through the first or second door, they may well go somewhere else.
ISO 42001 is more approachable than many expect
A common misconception is that ISO 42001 is purely an AI or IT security standard. In reality it is about how a school governs AI across the whole organisation, including where AI is used, the risks, accountability, and human oversight.
“Most schools think having an AI policy just means they’re covered. But the reality is policy is only one part.”
With around 38 core controls, and a shared foundation with ISO 27001, schools that have already begun their governance journey are often much further along than they think. When Andrew’s school moved from ISO 27001 to ISO 42001, they already had half of the work completed.
Essential Eight as a roadmap
Andrew shared a practical view: the full Essential Eight may not be realistic in every school environment, given shared devices, legacy systems, and specialist teaching tools. Used as a roadmap, alongside ISO 27001 as the governance standard, it forms what he calls a “pincer movement” that delivers strong protection while keeping schools workable.
Your 90 day starting point
Andrew’s advice for IT leaders was to avoid feeling overwhelmed and to start with three steps:
- Establish visibility: understand your data, its location, its sensitivity, and the controls around it. Build a supplier and software register.
- Establish ownership: name the people accountable for decisions about that data.
- Run a gap assessment against a framework or standard, then build a realistic roadmap rather than a giant list of controls.
“Don’t be overwhelmed. Don’t feel like you’re failing if you haven’t suddenly solved world hunger. This is a long process, but start with the basics.”
The key is continual improvement. Governance is a journey, and Andrew reminded us that most schools are already doing more than they realise:
“Most schools actually do more than they realise. It was just that we didn’t have them documented in a way, or the evidence available to collect.”
How GuardWare supports the journey
GuardWare is an Australian data security vendor helping organisations govern and protect information end to end. Discover finds and classifies sensitive data across M365, Google Workspace, file servers, and email. Insight gives visibility into data movement and AI usage, with real time user education that helps change behaviour. Protect applies persistent encryption so files stay secure even if they are lost or stolen.
As Rizwan summed up at the close of the session: governance can be simplified, and it doesn’t have to be a mountain that feels unconquerable.
Watch full webinar:
To talk to GuardWare about a data discovery exercise or the GuardWare Assessor offer,
Related Blogs
The Outsourcers Answer: TCS and HCLTech Confront a Hacker’s Claims
Eight Agents, Four Days: AI Runs a Government Intrusion in Taiwan
Closer to Home: Origin Energy’s Breach Traced to a Manila Call Centre
284 Million Rows in Four Days: McKesson’s Cloud Warehouses Emptied
How an SME Built a Security Posture That Enterprise Clients Trust