- September Edition
- Reading time~ 2mins
THE BIG DEAL
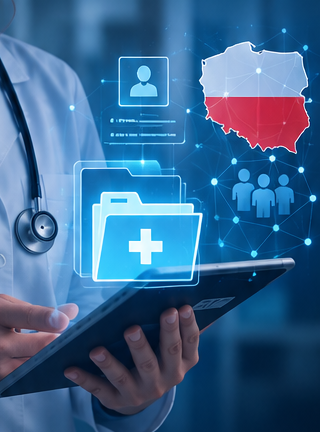
Poland’s Digital Affairs Minister confirmed on 12 August that attackers had taken more than 2.5 terabytes from MyDr, the electronic medical records supplier used by some 12,000 clinics, covering almost 19 million people, close to half the population. The haul spans PESEL national identity numbers, prescriptions, appointments, medications and documents patients handed to their doctors; the intruders sent journalists a screenshot of a senior politician’s file to prove it. The stolen material was historical data held through April 2024, kept long after the consultations it recorded had ended. The privacy regulator UODO has opened an inspection, and the government has warned that clinics themselves may face GDPR penalties.
TAKEAWAY Data retained past its purpose is a liability waiting for a buyer. Set retention rules that actually delete, encrypt whatever archive remains, and treat a supplier’s database as your own exposure, because the regulator will.
INSIGHT flags data retained past its useful life, like 2024 records still live in 2026, before a regulator or attacker finds it first.
Related Blogs
Eight Agents, Four Days: AI Runs a Government Intrusion in Taiwan
Closer to Home: Origin Energy’s Breach Traced to a Manila Call Centre
284 Million Rows in Four Days: McKesson’s Cloud Warehouses Emptied
How an SME Built a Security Posture That Enterprise Clients Trust
What If Your Data Could Protect Itself? A Data-First Security Playbook
Payment Security Summit & Gala – Australia 2026
Do you know where your sensitive data is?
Stop your IP and Design files from being stolen?