Data Security Posture Management plus Persistent Encryption.
The only approach that finds your sensitive data, monitors how it moves, and keeps it protected even after it leaves your control.

DSPM
-
Find sensitive data.
-
Understand exposure.
-
Monitor how it moves.

DLP
-
Detect risky handling.
-
Stop data leaving without authorisation.
-
Automates user education.

DSPM + PE
-
Do both - then encrypt every file so theft becomes irrelevant.
Risk management for all businesses


Most DSPM platforms stop at visibility. GuardWare doesn't.
No other vendor does all three.
If Microsoft 365 is your primary data environment
Full control of your M365 environment
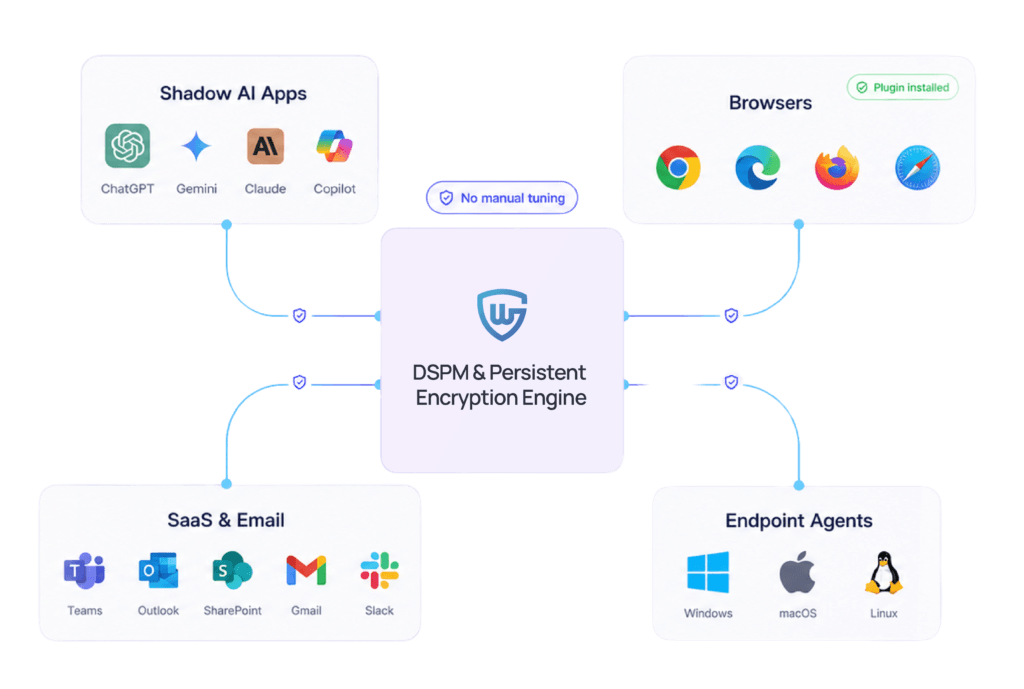
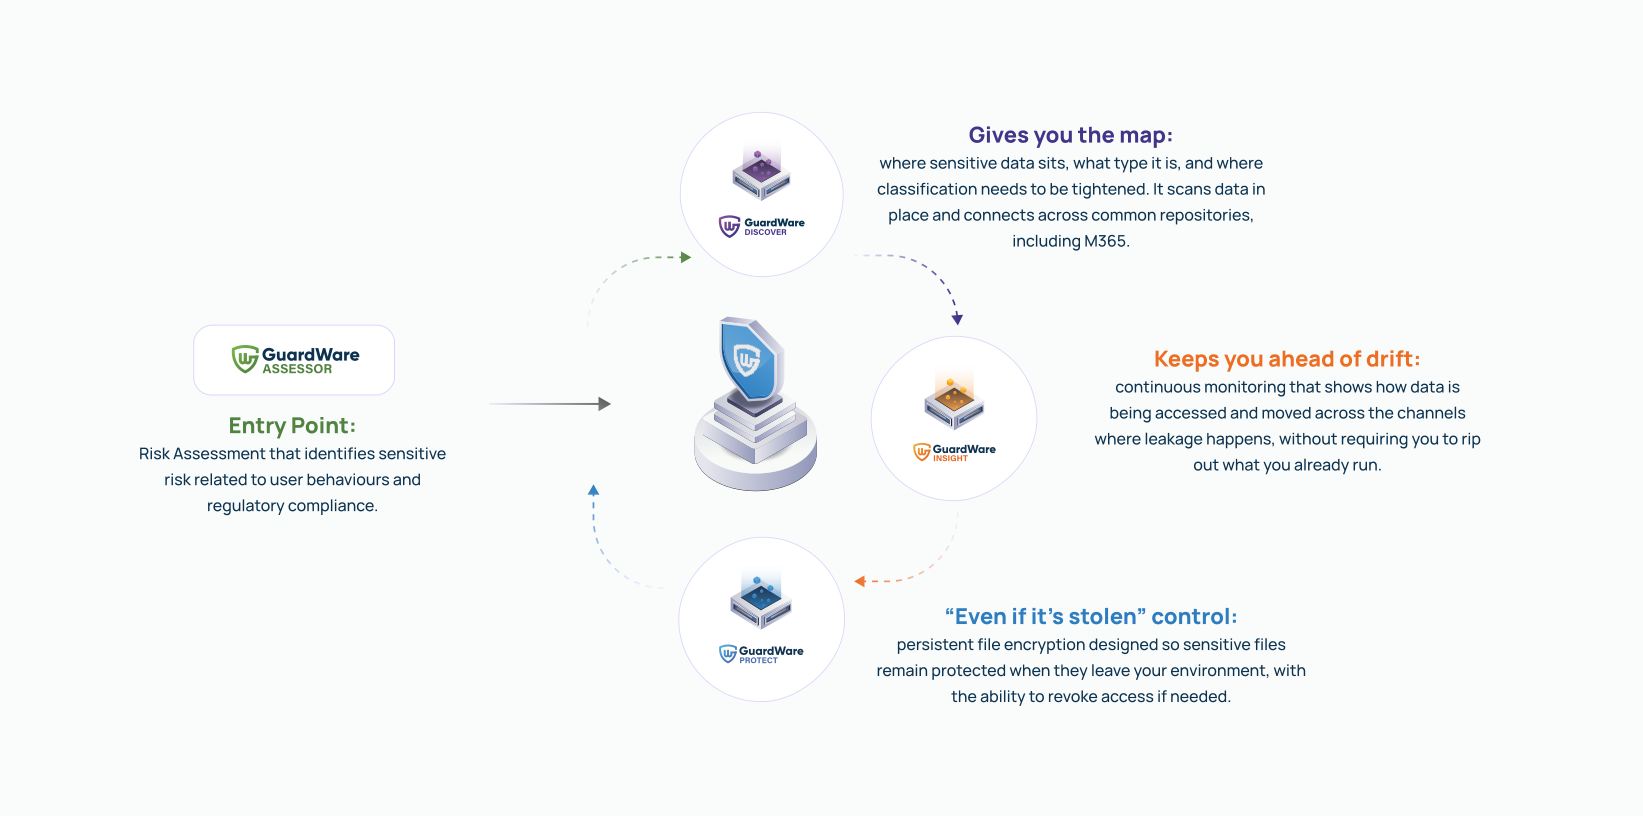
GuardWare connects directly to SharePoint, OneDrive, Teams, and Exchange. DISCOVER finds and classifies sensitive data. INSIGHT monitors how it moves. PROTECT keeps it encrypted even after it leaves. No agents. No disruption. Complete visibility from day one.
Find your exposure. Then fix it.
M365 Risk Snapshot
A starting point that shows priority locations and risky sharing patterns across Microsoft 365.
What you will get
-
A ranked list of your highest-risk M365 locations
-
The main exposure patterns - org-wide access, external links, over-permissioned folders
-
Practical next actions mapped to GuardWare pathways

Data Discovery Scan
For broader environments or higher data volumes. A hands-on scan that shows you exactly where your risk sits and what to fix first.
What you will get
-
Sensitive data hotspots across your environment, mapped and ranked
-
A prioritised remediation plan based on exposure and impact
-
A clear pathway into monitoring and enforcement where needed
GuardWare is the only vendor delivering data discovery, continuous monitoring, and persistent file encryption in a single integrated platform.
INSIGHT complements your existing DLP—closing blind spots with real-time behavioral monitoring that turns incidents into insights, not headlines.

Built from evidence, not assumptions.
DISCOVER gives IT and security leaders the ability to locate sensitive data across the organisation and understand exactly where controls need to be tightened, without disruption to existing operations.
Scans file in place
Identifies PII, PCI, PHI, cardholder data, and business-sensitive content across files, text, and images. Works across Windows, Linux, M365, and legacy file shares.
M365 email and SharePoint
When a protected file is accessed by an unauthorised party, through a breach, through exfiltration, through a compromised supply chain, they cannot read it. It cannot be used as leverage in a ransomware demand. It cannot be published to cause reputational damage. It is, in every meaningful sense, worthless to them.
Remediation Workflows
The keys that unlock it are yours. And when you need to revoke access, you can do so remotely, immediately, without any physical interaction with the file or the device that holds it.
Real time Dashboard
The keys that unlock it are yours. And when you need to revoke access, you can do so remotely, immediately, without any physical interaction with the file or the device that holds it.


Every channel covered.
Every risk visible.
Next-gen DLP built for the reality of 2026, where data moves across endpoints, cloud platforms, personal devices, AI tools, and home networks, often simultaneously
24-hour monitoring
Endpoint DLP Monitors data activity on corporate devices, file transfers, application usage, USB connections, print activity, and screen capture,
Alert and Email right people
Automated User education
Stressless Integrations


Your data, Under your control wherever it goes.
PROTECT applies persistent file encryption so that sensitive files remain protected after they leave your environment. The encryption travels with the file. The control stays with you.
Persistent encryption
Protected files remain encrypted when stored anywhere, transferred by any method, and when in use by an authorised user or application.
Remote kill
Unique key per file
Works with Integrates Platform

Sharing design files, engineering drawings, or technical drawings with partners?

Sample Assessment Reports
Defence Supplier
Evaluates security readiness, risk awareness, and operational resilience in defence environments.
Corporate and NFP
Education
Reviews data protection practices and digital safety awareness in educational settings.
What a CISO gets from GuardWare DSPM.
Most DLP tools respond to a breach. INSIGHT prevents the next one.
Real-time Alerts
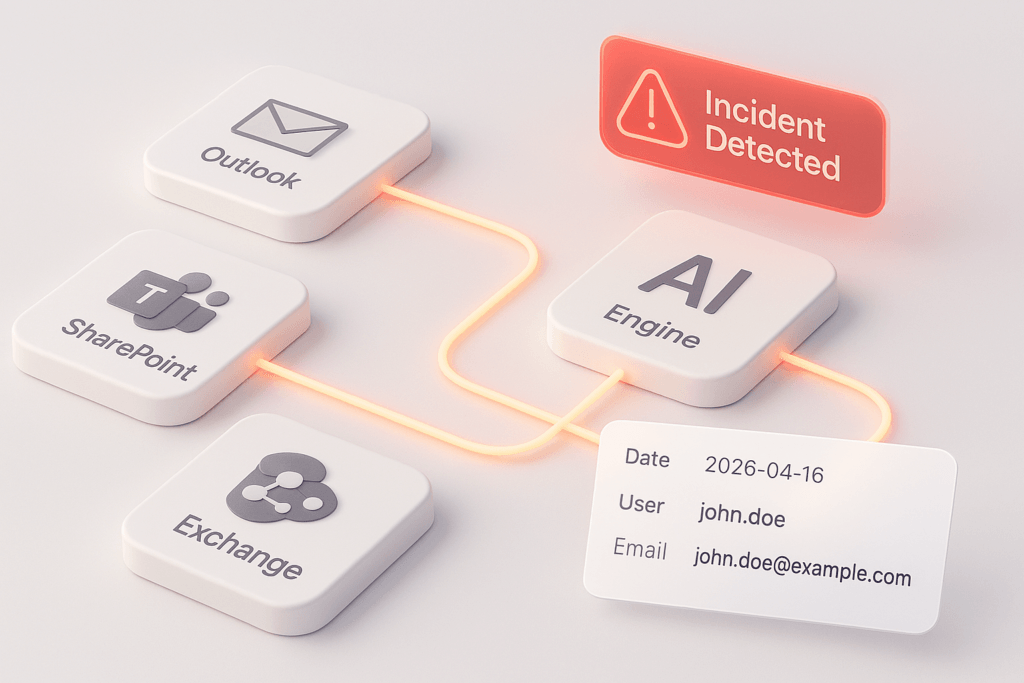
When an employee makes a risky decision with sensitive data, INSIGHT notifies them, their manager, and the security team simultaneously, at the moment the event occurs, not after it has escalated.
A security culture that builds itself
Automated user education triggered in context changes behaviour from the inside out. Every risk event becomes a teachable moment, without blocking access, creating friction, or adding to your team's workload.
Evidence ready for any regulatory conversation
INSIGHT's audit trail gives you documented evidence of what was detected, what was escalated, and what action was taken, without scrambling to reconstruct a timeline after the fact.
Visibility into your AI risk exposure.
Shadow AI is already happening across your organisation. INSIGHT identifies what tools are being used, what data is being fed into them, and where your unsanctioned AI exposure sits, so you can manage it before it becomes an incident.

Why GuardWare Data-Centric Platform
Traditional DLP was built for a world with a clear boundary, a corporate network, a managed device fleet, a predictable set of applications.
0%
average cost of a data breach in Australia. The cost of not knowing is higher than the cost of watching. (IBM, 2024)
0
data breach notifications in Australia in 2024, the highest annual number since the NDB scheme began. (OAIC, 2024)
$0M
average cost of a data breach in Australia. The cost of not knowing is higher than the cost of watching. (IBM, 2024)
Start with a clear view,
then extend control
Most DLP tools respond to a breach. INSIGHT prevents the next one.
Deep Content Scanning
Identifies PII, PCI, PHI, cardholder data, and business-sensitive content across files, text, and images. Works across Windows, Linux, M365, and legacy file shares.
Remediation Workflows
Classify, quarantine, or delete sensitive data. Decentralised remediation alerts go directly to data owners, with IT security oversight maintained throughout.
Classification & Tagging
Rule-based classification so data owners can remediate and apply governing controls. Reduces the burden on IT by delegating classification at the source.
24-hour monitoring
Endpoint DLP Monitors data activity on corporate devices, file transfers, application usage, USB connections, print activity, and screen capture, 24 hours a day, whether the device is in the office or at home.
AI Tool Visibility
Detects and monitors the use of AI applications and web-based AI tools, including shadow AI, across corporate and personal devices. Identifies when sensitive data is being fed into unsanctioned platforms.
User Activity & Cyber Awareness
Automated user education triggered at the point of risky behaviour. Employees receive contextual guidance in real time, building a security culture from the inside out, rather than relying on annual training that people forget by Thursday.
Powerful Policy Creation with Flexible Data
Combine ready-to-use data types with custom definitions for complete control and accuracy.
Real-Time Visibility for Confident Compliance
INSIGHT's audit trail, real-time alerts, and documented evidence base support regulatory compliance across the frameworks that matter most to Australian enterprise.

Common Questions
INSIGHT
INSIGHT Lite
Does INSIGHT replace our existing DLP tools?
No. INSIGHT is designed to work alongside your existing security investment, not replace it. It closes the blind spots most tools leave open, particularly across AI tools, personal cloud storage, work-from-home environments, and shadow IT, adding the monitoring layer that covers channels your current stack cannot reach.
How quickly is INSIGHT operational?
INSIGHT deploys quickly without disruption to existing infrastructure. For M365 environments, native API integration means the monitoring layer is active from day one. Endpoint agents deploy to corporate devices with no impact on how your people work.
What AI tools does INSIGHT monitor?
INSIGHT monitors browser-based and application-level AI tools including ChatGPT, Copilot, Claude, and other third-party AI services. It identifies when sensitive data is being processed by unsanctioned AI applications and alerts security teams in real time.
What happens when a risky event is detected?
INSIGHT notifies the employee, their manager, and the security team simultaneously at the moment the event occurs, not in the next daily report. It also triggers automated contextual user education at the point of the event, driving behaviour change in real time. Where your policy requires it, INSIGHT can block the transfer before it completes.
What evidence does INSIGHT produce for compliance and audit purposes?
Every event, every alert, and every action taken is logged in a complete audit trail. INSIGHT produces the documented evidence your security team needs for internal governance, regulatory response, and supervisory review, without needing to reconstruct a timeline after the fact.
Is INSIGHT a DLP product?
INSIGHT is next-generation Data Loss Prevention built for the reality of 2026, where data moves across endpoints, cloud platforms, personal devices, AI tools, and home networks simultaneously. It goes beyond traditional DLP by adding real-time behavioural monitoring, automated user education, and AI tool visibility across every channel where data leakage actually happens.